CVE-2025-12907
Overview
Background
- "Copy as cURL (cmd)"
- a DevTools Network panel context-menu action that turns a recorded request (URL, headers, body) into a
curlcommand line meant to be pasted into the Windows command prompt. - `escapeStringWin`
- the helper in
front_end/panels/network/NetworkLogView.tsthat quotes each request-derived string forcmd.exe, wrapping it inencapsCharsand escaping metacharacters with^. - Caret escaping
- in
cmd.exe,^escapes the next character so the shell treats it literally instead of as syntax or a delimiter. - `\s` vs. special whitespace
- the JavaScript
\sclass covers space,\rand\n, and also tab, vertical tab, form feed and other Unicode whitespace.
Root Cause Analysis
escapeStringWin escapes request data with a chain of .replace() calls. The main one, .replace(/[^a-zA-Z0-9\s_\-:=+~'\/.',?;()*]/g, ‘^$&’), caret-escapes every character not on an allow-list. That allow-list includes all of \s, so tabs, vertical tabs, form feeds and other non-space whitespace passed through unescaped. Space, \rand\nhad their own handling (newlines are rewritten by the last.replace(/\r?\n|\r/g, ‘^\n\n’)`). According to the commit message, the Windows command prompt treats these special whitespace characters as delimiters. Server- or page-controlled data such as a URL, header or body containing them could therefore end up outside the intended single argument when the generated command is pasted.
The fix adds .replace(/[^\S \r\n]/g, '^$&'). The class [^\S \r\n] matches any whitespace except space, CR and LF, and the replacement caret-escapes each match before the newline rewrite runs. This tightens the sanitisation.
\s class as safe. In cmd.exe, though, tabs and other non-space whitespace work as separators. The fix caret-escapes every whitespace character other than space, CR and LF.Attack Path
- Attacker-controlled request data A malicious site makes the browser send a request whose URL, headers or body include special whitespace (for example a tab or vertical tab) next to attacker-chosen text.
- Victim copies the request
A developer on Windows opens DevTools, finds the request in the Network panel and uses “Copy as cURL (cmd)”, which runs
escapeStringWinon the request fields. - Unescaped delimiter in output
Before the fix, the special whitespace was copied into the command unescaped, so the “quoted” string no longer formed one intact argument once
cmd.exeparsed it. - Argument/command injection on paste (inferred)
When the victim pastes and runs the command, attacker text after the delimiter may be read as extra
curloptions or shell input. This could cause unintended actions on the local machine(inferred); the exact effect is not shown in the patch.
Impact Assessment
cmd.exe. Ordinary web content can supply the malicious request data, and no compromised renderer, flag or extension is needed. Local command or argument injection is the likely worst case (inferred). The vendor rates this low (“Insufficient validation of untrusted input in Devtools”). The provided metadata does not say whether it was exploited in the wild.Files Changed
AUTHORSfront_end/panels/network/NetworkLogView.ts
Audit Directions
- Allow-lists built on broad character classesReview other shell-escaping helpers in DevTools (“Copy as cURL (bash)”, “Copy as PowerShell”, “Copy as fetch/Node.js”) for allow-lists that include
\s,\wor Unicode ranges which the target shell or parser treats specially. - Order of chained replacementsIn multi-step escapers, check that a later
.replace()cannot create or re-expose a character an earlier step meant to neutralise, for example by inserting^,"or newlines. - Request data turned into executable textAudit any feature that exports network data (HAR, scripts, command lines) for incomplete escaping of attacker-controlled URL, header and body fields.
Patch
From 553969206ce9e85d4f11dbe4756ddcfd1366e731 Mon Sep 17 00:00:00 2001
From: Ameen <ameenbasha111@gmail.com>
Date: Tue, 22 Jul 2025 16:33:11 +0530
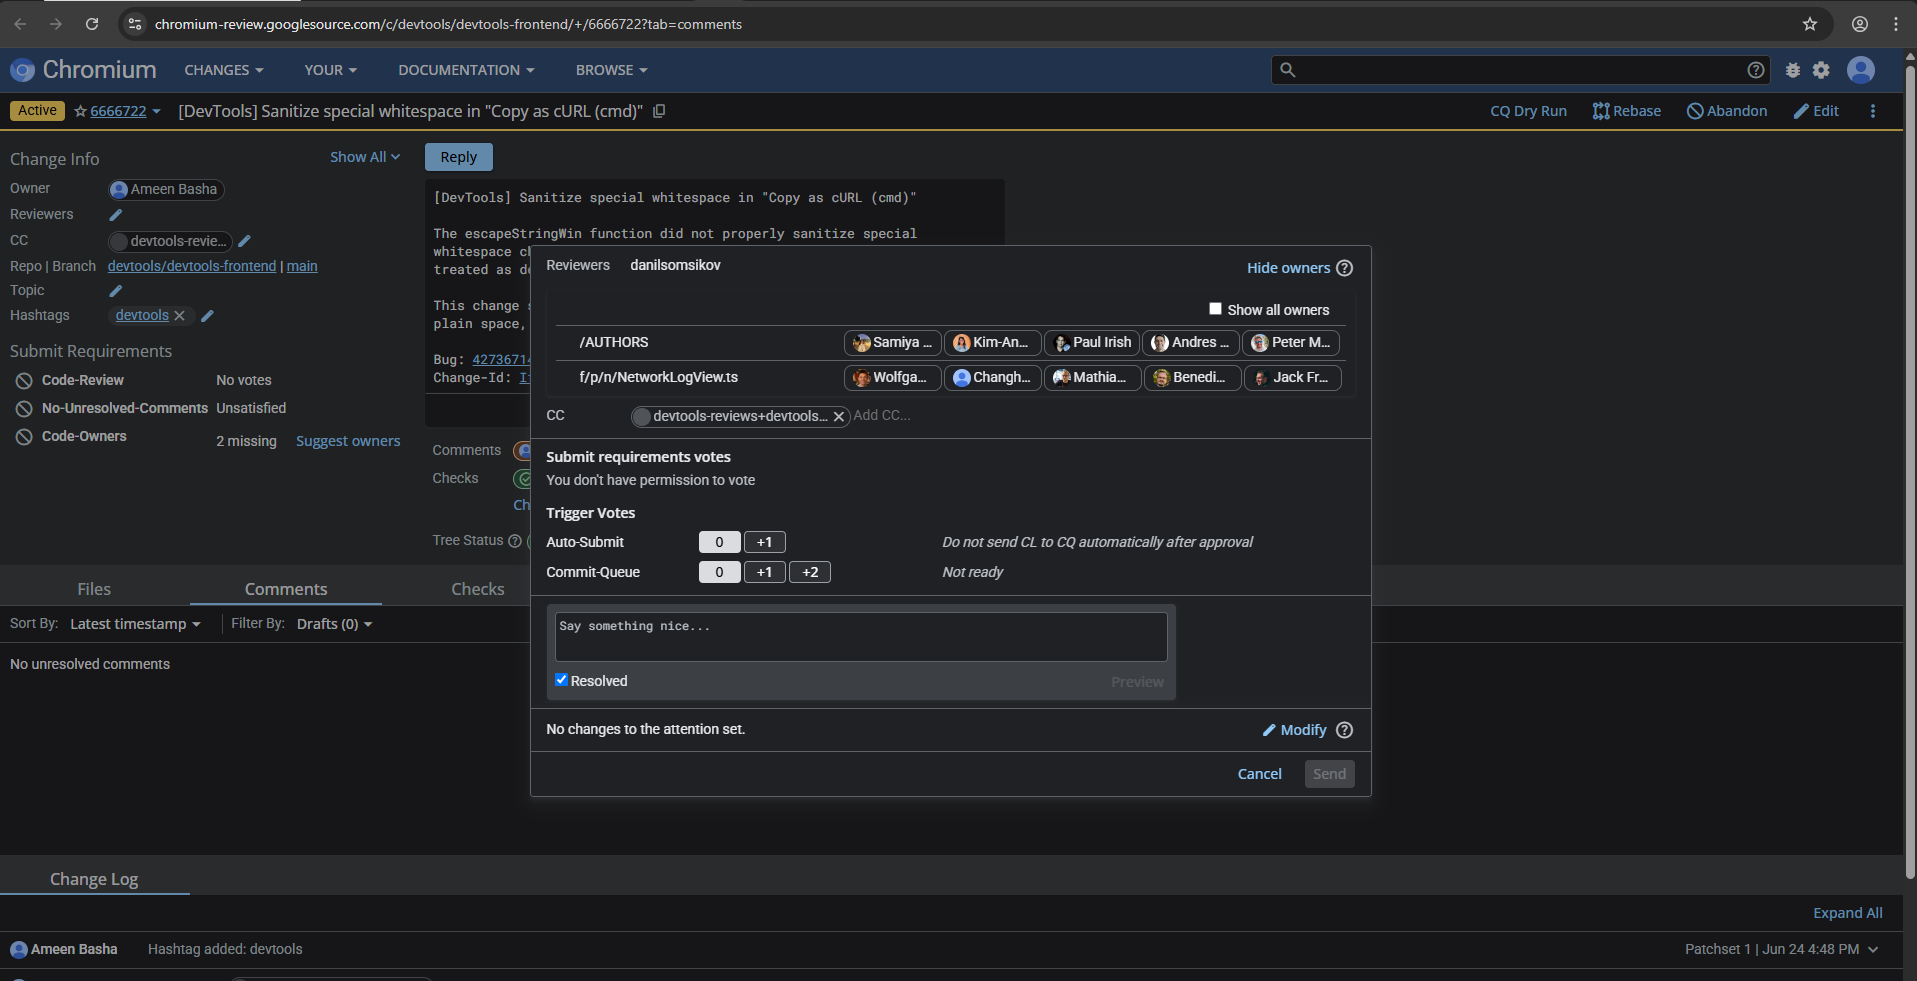
Subject: [PATCH] [DevTools] Sanitize special whitespace in "Copy as cURL (cmd)"

The escapeStringWin function did not properly sanitize special
whitespace characters (e.g., tabs, vertical tabs), which are
treated as delimiters by the Windows command prompt.

This change sanitizes all whitespace characters (other than normal space), which closes the vulnerability.

Bug: 427367145
Change-Id: If1f1be803a4b4a20a93b6982247eaf9cbebaf6ce
Reviewed-on: https://chromium-review.googlesource.com/c/devtools/devtools-frontend/+/6746171
Reviewed-by: Simon Zünd <szuend@chromium.org>
Commit-Queue: Simon Zünd <szuend@chromium.org>
Reviewed-by: Danil Somsikov <dsv@chromium.org>
Commit-Queue: Danil Somsikov <dsv@chromium.org>
---

diff --git a/AUTHORS b/AUTHORS
index 2de9dac..7061bb3 100644
--- a/AUTHORS
+++ b/AUTHORS
@@ -16,6 +16,7 @@
 Alesandro Ortiz <alesandro@alesandroortiz.com>
 Alexander Stammbach <alexander@stammbach.io>
 Alexey Rodionov <fluorescent.hallucinogen@gmail.com>
+Ameen Basha <ameenbasha111@gmail.com>
 Ankit Mishra <ankit.mishra131990@gmail.com>
 Anna Agoha <annaagoha@gmail.com>
 Anthony Xie <anthonyxie64@gmail.com>
diff --git a/front_end/panels/network/NetworkLogView.ts b/front_end/panels/network/NetworkLogView.ts
index e44d26f..27d1648 100644
--- a/front_end/panels/network/NetworkLogView.ts
+++ b/front_end/panels/network/NetworkLogView.ts
@@ -2337,6 +2337,7 @@
               .replace(/"/g, '\\"')
               .replace(/[^a-zA-Z0-9\s_\-:=+~'\/.',?;()*`]/g, '^$&')
               .replace(/%(?=[a-zA-Z0-9_])/g, '%^')
+              .replace(/[^\S \r\n]/g, '^$&')
               .replace(/\r?\n|\r/g, '^\n\n') +
           encapsChars;
     }
Original Bug Report
Command injection in "Copy as cURL (cmd)" due to improper sanitization
Steps to reproduce the problem
- Open the poc html in chrome
- open network teab and copy the requests with - copy all as curl (cmd) feature
- paste the command on cmd you can see the calc popup
Problem Description
A command injection vulnerability exists in the DevTools “Copy as cURL (cmd)” feature on Windows. The current implementation correctly handles carriage returns (\r) but fails to sanitize the tab character (\t).
The cmd.exe shell interprets the tab character as a delimiter, similar to a space. By injecting a payload containing a tab followed by a command separator (e.g., &) and a newline sequence, an attacker can break out of the intended cURL argument and execute arbitrary commands when the copied text is pasted into a Windows command prompt.
This is a bypass of a previous security fix that only addressed newline characters.
Additional Comments
Security Impact: This vulnerability allows for arbitrary code execution on a user’s machine. If a user is tricked into pasting a crafted cURL command from a malicious source, the attacker can execute commands with the user’s privileges.
Note: I have attached the poc video and html file for reference
Summary
Command injection in “Copy as cURL (cmd)” due to improper sanitization
Custom Questions
Reporter credit:
Ameen Basha M K
Additional Data
Category: Security
Chrome Channel: Canary
Regression: N/A \